Cose
Designing PIC-X: Centralized Token Exchange End to End
reading time: 16 minutes
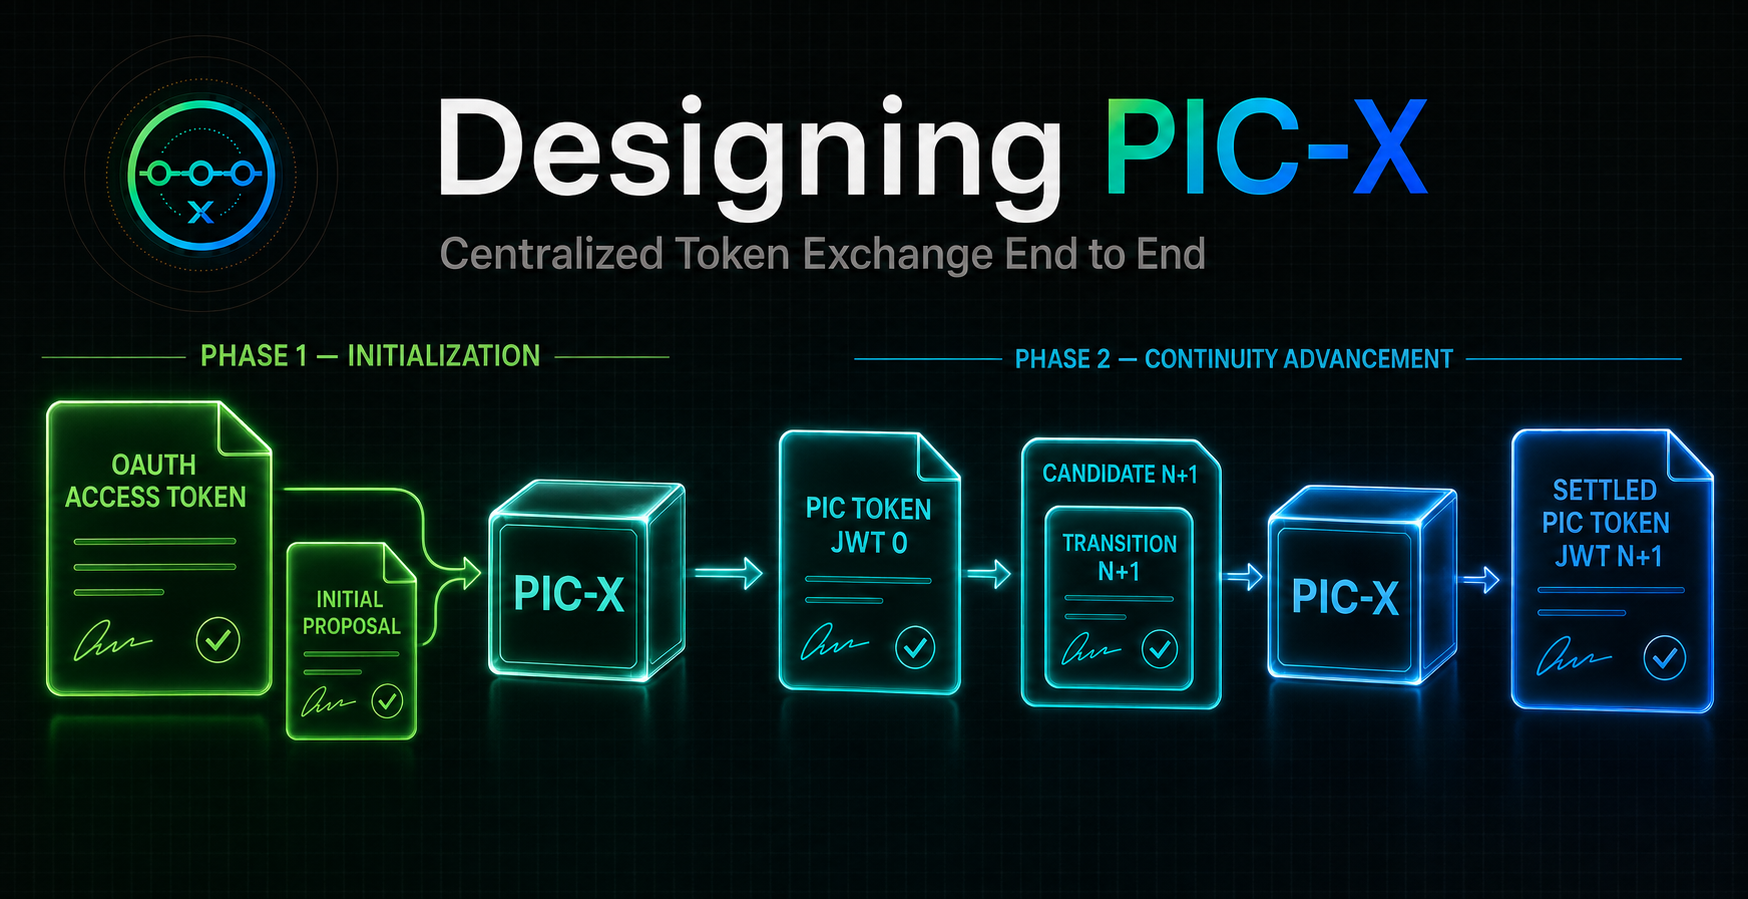
PIC Profile 0.2 defines centralized PIC-X-mediated authority continuity.
This walkthrough follows one sensitive-document execution from OAuth authority into PIC Token JWT 0, then through two workload-produced candidate transitions.
OAuth authority
        |
        v
PCA 0
{ read document-42, save }
        |
        | Worker 1 reads document-42
        | remove read authority
        v
PCA 1
{ save }
        |
        | Worker 2 stores the result
        | remove save authority
        v
PCA 2
{ no execution invariants }
Cryptographic byte values, compact tokens, signatures, hashes, and COSE byte strings below are illustrative. The structure and field semantics follow Profile 0.2.
Designing PIC-X: PIC Token JWT and COSE Artifacts
reading time: 16 minutes
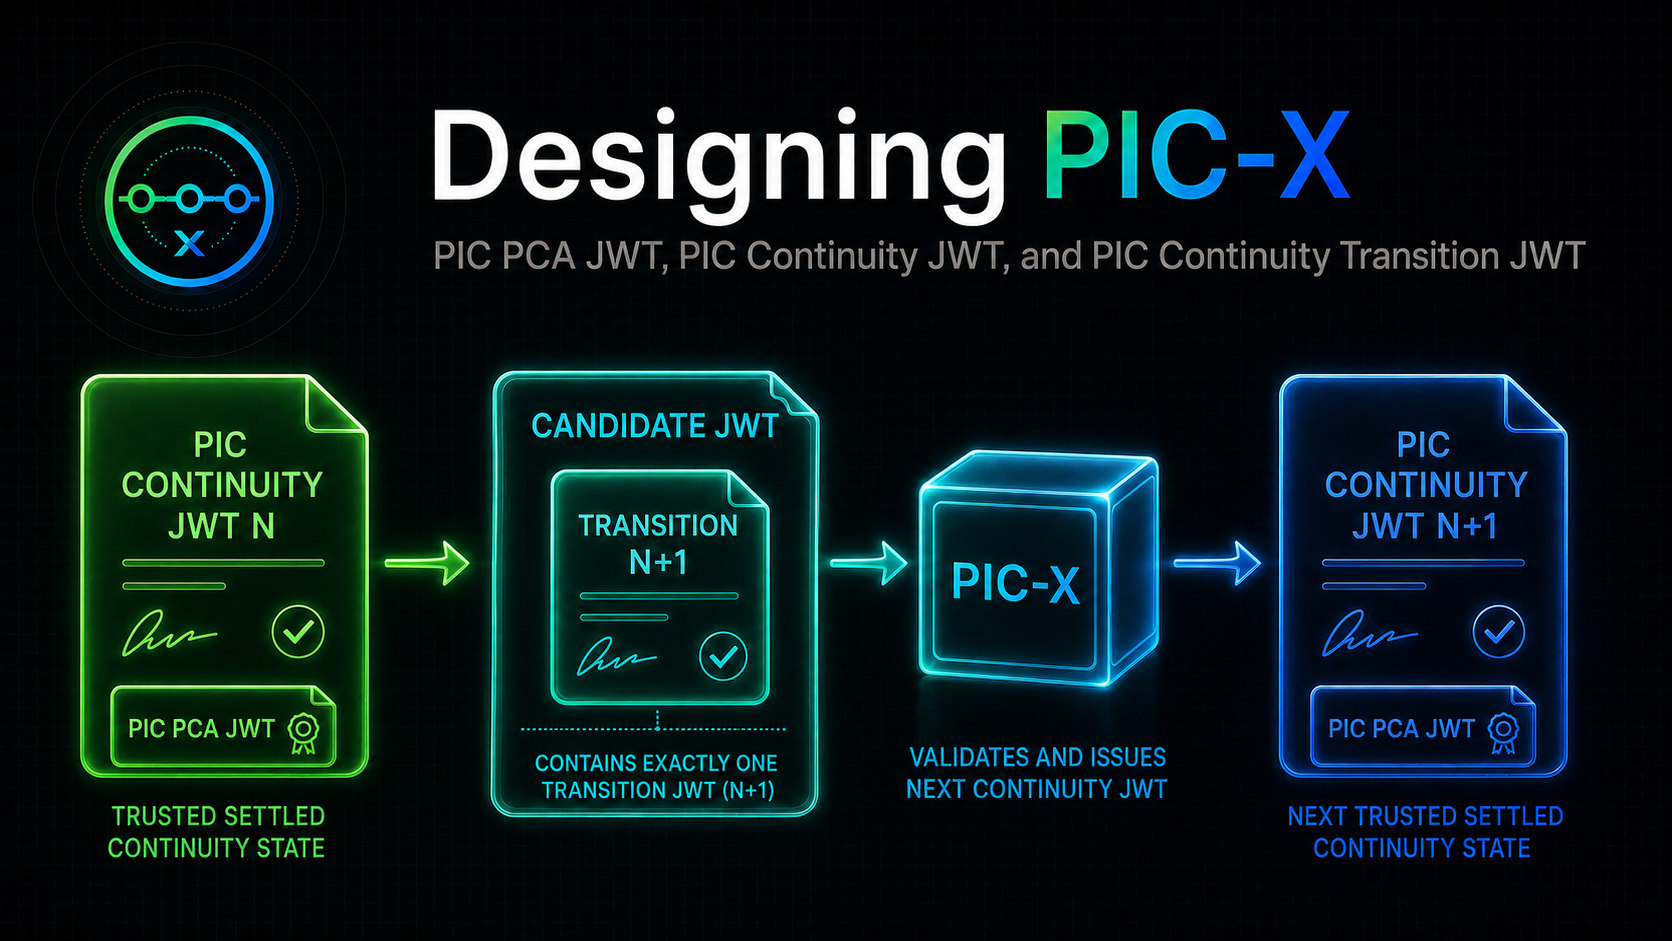
PIC Profile 0.2 defines centralized PIC-X-mediated authority continuity.
The active profile is:
https://pic-protocol.org/profiles/0.2
This article defines the external PIC Token JWT envelope and the native COSE artifacts used by that profile.
OAuth access token + Initial Continuity Proposal
        |
        v
PIC-X
        |
        v
realm-signed PIC PCA COSE 0
        |
        v
realm-signed settled PIC Continuity COSE 0
        |
        v
realm-signed PIC Token JWT 0
Non-initial advancement is candidate-based: